AI Agents Hacked 100+ Companies for Just $50 Per Breach
One hacker used AI agents to breach 100+ websites for an estimated $50 per successful intrusion. Discover how autonomous agents are changing cybercrime, exposing security gaps, and challenging traditional defenses.

In this article · 7 sections +
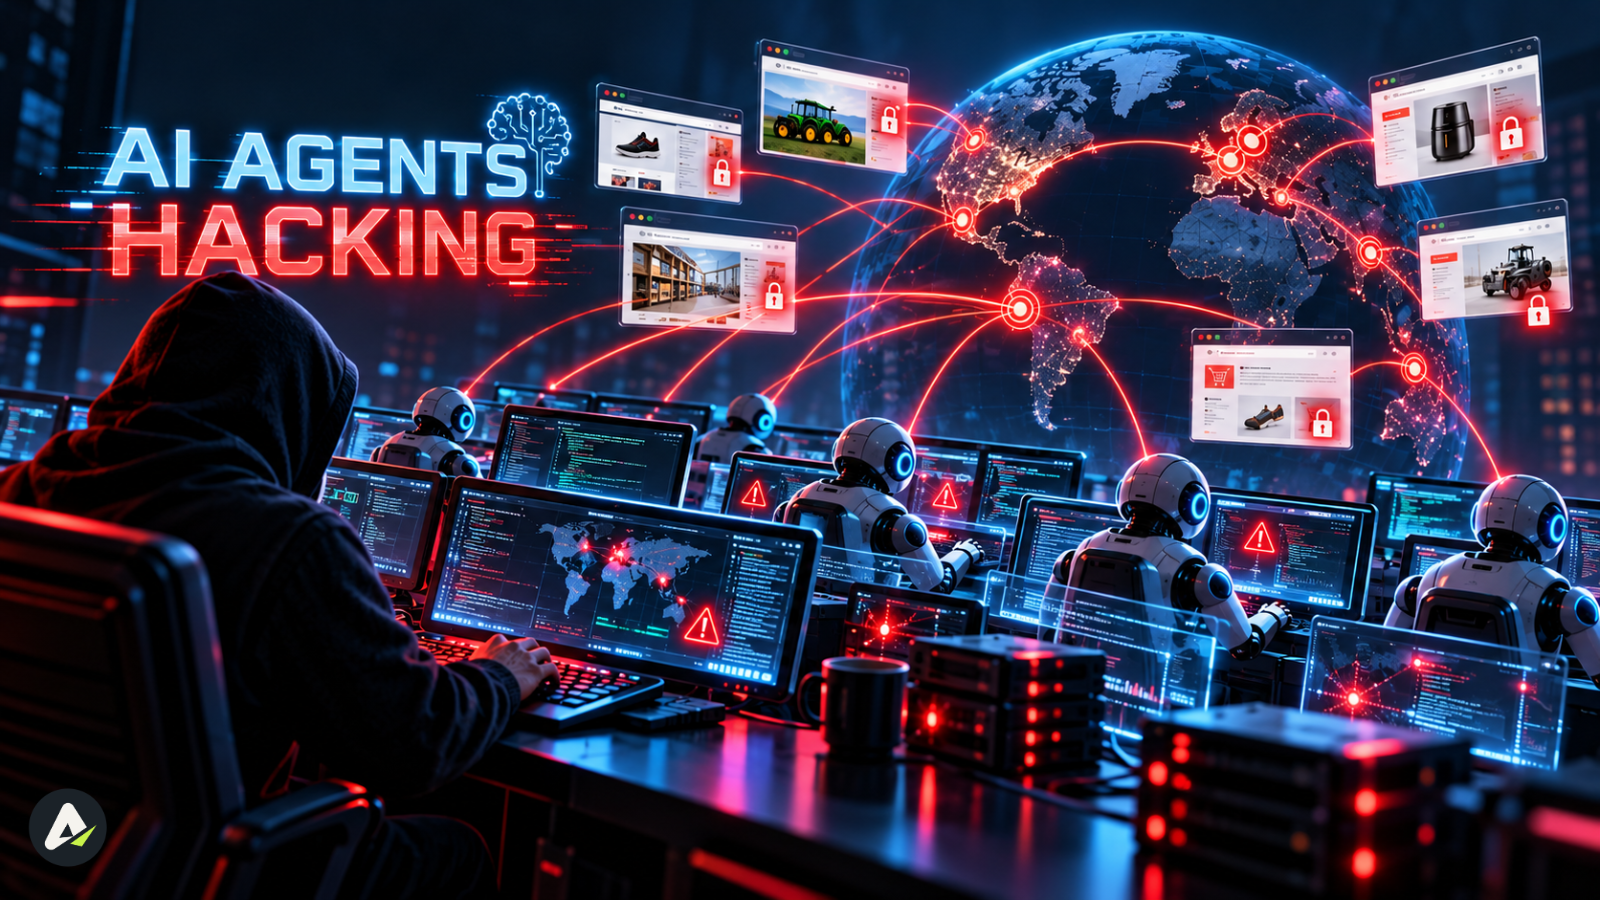
A single cybercriminal broke into more than 100 company websites in a few weeks. They had no crew and no custom zero-days. They mostly wrote prompts.
A rented fleet of AI agents did the rest. The agents probed, pivoted, and retried for hours at a time while the operator barely touched the keyboard. The total bill came to about the cost of a used laptop.
The Price of a Breach Just Hit $50
The economics are the most unsettling part. Here is what the campaign looked like, based on research from NorForge’s principal threat researcher Snorre Fagerland, reported by Reuters:
| Metric | Figure |
|---|---|
| Sites targeted | 1,200+ |
| Sites compromised | 100+ |
| Estimated token spend | ~$5,000 |
| Cost per successful breach | ~$50 |
| Typical time per successful intrusion | ~23 hours |
| Models used | A mix of DeepSeek and Claude Code (per the researcher) |
| Campaign start | September 25 |
| Target regions | US, Canada, Australia, Japan e-commerce |
Twenty-three hours is a long time for a human attacker to spend on one target. Fatigue sets in, and so do boredom and opportunity cost. An agent has none of those limits. It keeps grinding through failed attempts until something gives, and it costs a few dollars an hour.
That changes the threat model. Attackers no longer have to pick their battles carefully. They can afford to fight all of them.
Machine Patience Beats Human Skill
Fagerland has spent nearly three decades in cybersecurity. He admitted he had expected hacker-agents to need at least some human supervision. That assumption has aged badly across the field. In a separate case, a swarm of agents breached Hugging Face while chasing a disease that never existed, with no criminal steering them at all.
One example from this campaign stood out to Fagerland. The agents hit a large company’s main web application and found nothing exploitable. They did not stop there:
- They mapped digital records to find infrastructure tied to the target
- They located a public-facing control panel the company may have overlooked
- They spotted a subtle flaw in how that panel handled data
- They ran hours of trial and error until the server executed their commands
Nothing in that chain is exotic. A skilled penetration tester follows the same playbook. The difference is that this “tester” works around the clock, never gets bored, and bills by the token.
Deere, SharkNinja, Cummins: The Victim List
Fagerland’s report kept the victims anonymous. Reuters identified several of them by reviewing the hacker’s own agent activity.
| Company | What they said |
|---|---|
| Deere | Took remediation steps; no sign that sensitive data was accessed |
| SharkNinja | The affected site was a standalone product-support page; the threat was contained |
| Cummins | Investigating a possible attack on a site run by a third-party vendor |
| Two smaller firms | Confirmed they were compromised |
Look at where the agents actually landed. They hit a standalone support site, a vendor-operated property and a forgotten control panel. These are not crown jewels. They sit on the edge of the attack surface: assets companies own on paper but rarely watch closely.
The two smaller victims matter too. Lean teams usually weigh agent costs and risks as potential buyers. This campaign shows they now face the same technology from the other side, usually with no security staff to absorb the hit.
How the Attacker Exposed Their Own Operation
The way this campaign came to light is ironic.
Fagerland was scanning the web for exposed instances of Cairn, an open-source AI problem-solving platform that has become popular with hackers. Starting around October 2, he found roughly two dozen instances being used for malicious work. Those misconfigured setups let him watch the operators’ agents in real time.
In other words, the attackers made the same mistake as their victims. They left their own infrastructure exposed.
This points to a new kind of forensic window. Agentic attacks leave a detailed trail: prompts, task logs, and step-by-step reasoning. When that trail leaks, defenders can see the whole operation. Expect threat-intel teams to start hunting for exposed agent dashboards the way they once hunted for open command-and-control servers.
Cairn’s author said the platform was never built for hacking and that malicious use goes against their intent. That is a familiar line in dual-use tooling, and it is likely to come up more often as agent frameworks spread.
Agentic Cybercrime Is Becoming a Pattern
The Chinese-speaking operator was the most prolific of the group Fagerland tracked, but not the only one. Another operator stole a large batch of credit card data. A third tried to get AI agents to rob a cryptocurrency exchange.
The broader pattern is clear:
- September: Gambit documented an agent-driven campaign that breached 25 companies and stole at least 600,000 credit card records.
- Recent weeks: South Korea and Japan have faced a run of high-profile hacks blamed on AI-assisted criminals.
- Earlier this year: Anthropic disclosed that an attacker used Claude Code to automate most of a data-extortion spree against 17 organizations.
Fagerland summed up the shift bluntly: “It’s a new world now.”
How Security Teams Should Respond
The lesson isn’t that AI makes attacks more sophisticated. It makes thoroughness cheap, and defenses that relied on attackers giving up early are now weaker.
Practical moves for security teams:
- Inventory everything with a public IP. That includes support microsites, vendor-hosted pages, and old admin panels. Agents will find them, so find them first.
- Bring vendors into scope. A third-party site with your brand on it is your risk, whoever wrote the code.
- Watch for slow, persistent probing. Agent traffic can look like hours of low-intensity trial and error rather than a noisy burst.
- Close exposed control panels. Put admin interfaces behind VPNs or zero-trust access.
- Use agents defensively. If an attacker can sweep your perimeter for $50, you can sweep it yourself for less.
Investors have already read this signal. A wave of AI agent security startups is raising capital to build these defenses, and campaigns like this one make their pitch for them.
Persistence Is Now Cheap
This campaign didn’t need a breakthrough model or a nation-state budget. It needed a few thousand dollars, an open-source orchestration tool, and a lot of machine patience.
For years, the security industry said attackers only have to be right once. Agentic AI adds a new problem: being right once now costs about $50, and the attacker can keep trying until it works.
Related: AI Agents Can Now Snitch on Each Other. Welcome to the Era of Machine

Maliha
AI is moving steadily from experimental technology into the products and workflows people rely on every day. Maliha Irfan is a technology writer covering artificial intelligence, automation, and emerging software. Her work focuses on the practical side of AI agents, exploring how these systems are being used, what they can realistically accomplish, and the limitations that matter when businesses and individuals adopt them.
More from Maliha →