Claude Code Found a Crypto Miner Hiding on a Mac.
Claude Code uncovered a hidden XMRig crypto miner consuming roughly 12 CPU cores and pushing a developer’s Mac to 112°C. Discover how the AI coding agent detected the threat.

In this article · 7 sections +
A developer asked Claude Code for a simple Mac temperature monitor. It came back with a security incident report.
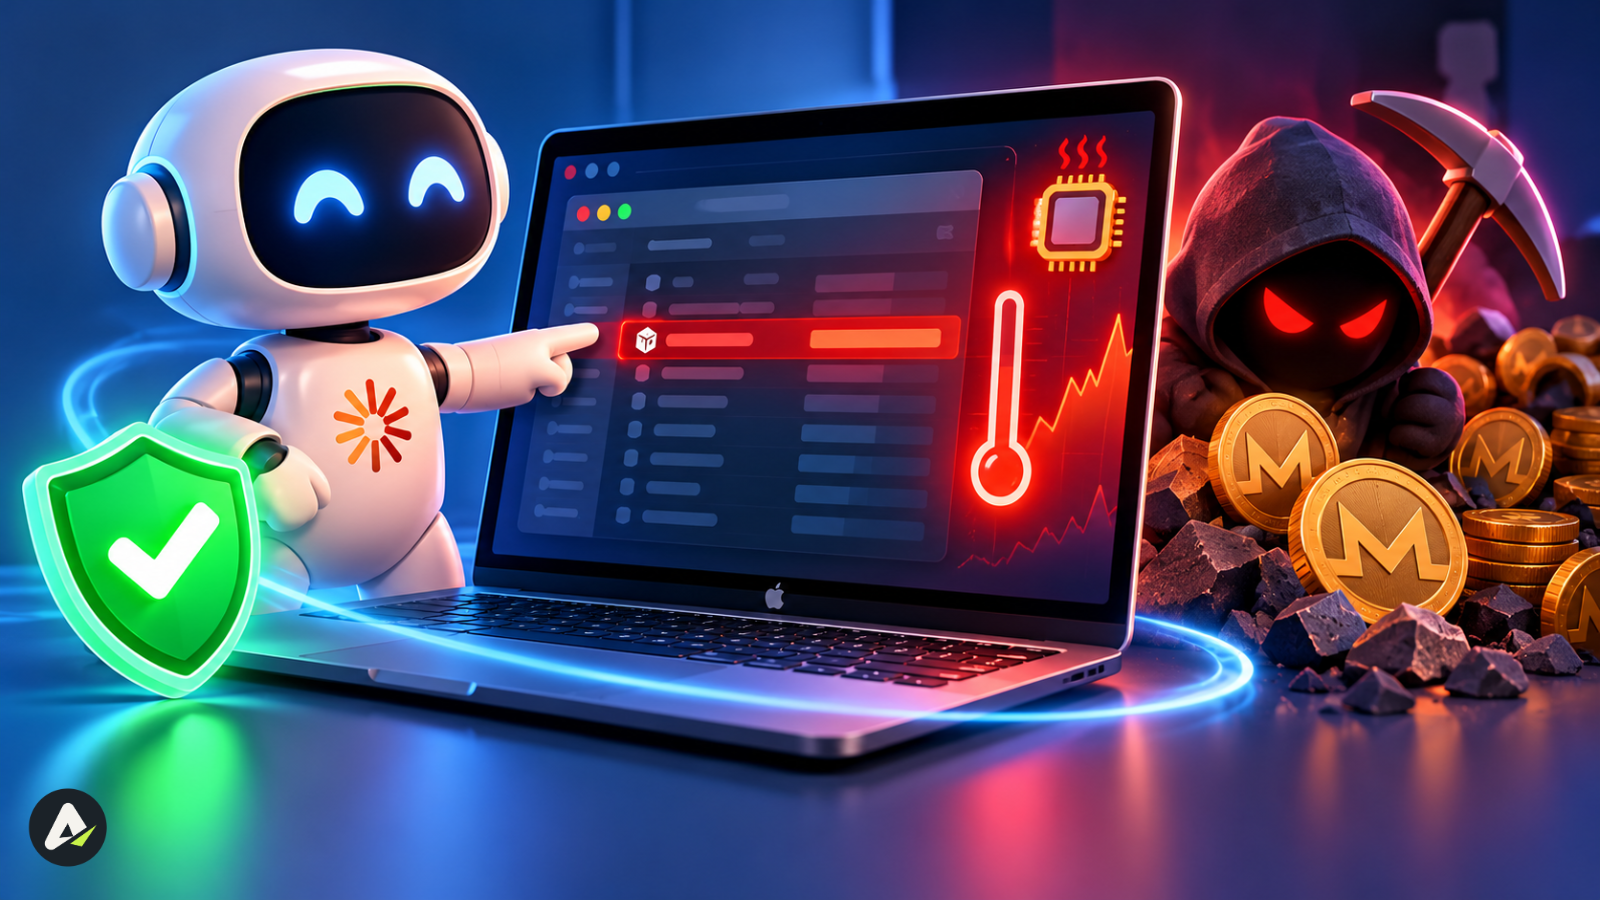
Partway through the build, the agent flagged something off-script. It wrote: “Your Mac is running a crypto miner that I didn’t put there.” The culprit was XMRig, an open-source Monero miner. It was eating about 1,175% CPU, roughly 12 cores’ worth, and pushing the chip to 112°C.
The developer, Reddit user UntilHEX, had been living with a sluggish, overheating Mac for weeks without knowing why. Now they knew.
What Actually Happened
The timeline, as reported by Tom’s Hardware and the original r/claude post:
- The trigger: UntilHEX dumped raw temperature sensor readings, and the numbers looked far too high.
- The diagnosis: Claude Code traced the heat to sustained heavy load, then to a specific process:
xmrig. - The persistence: The miner had hidden itself on the system and launched at startup. A screenshot suggests it joined the startup roster around August 29.
- The irony: The temperature app likely exists because of the infection. The developer was trying to figure out why the machine ran so hot.
| Detail | Reported value |
|---|---|
| Malware | XMRig (Monero miner) |
| CPU load | ~1,175% (about 12 cores) |
| Peak temperature | 112°C |
| Likely install date | August 29 |
| How it got in | Not disclosed |
The Agent Asked Before It Acted
The detection is the headline. The restraint is the bigger story.
Claude Code didn’t kill the process or delete anything on its own. It explained what it found and proposed a plan: stop the startup item, stop the miner, and move the files to a quarantine folder rather than wiping them. Then it waited for a yes.
That order of operations matters. A coding agent with shell access can do serious damage in a few seconds. Agents that have deleted the wrong directory have made headlines before. Here, the agent treated a live security finding as a decision for the human, not a task to finish.
Until HEX approved the cleanup. Claude handled almost all of it. One file needed manual deletion because the agent hit a permissions wall. A follow-up Malwarebytes scan then confirmed the system was clean.
That’s a sensible playbook for any agent with real system access: detect, explain, propose, wait, act, verify. Approval gates are fast becoming the core design question across agentic AI, from shell commands to agents that spend money.
Why an Agent Caught What the Owner Missed
The developer didn’t spot the miner. The agent did. That isn’t magic. It comes down to where the agent sits.
Coding agents work inside the terminal. They read process lists, sensor output, and system logs as routine context. A human glances at a hot laptop and blames Chrome. An agent sees xmrig at the top of the CPU column and recognizes the name.
This points to a quiet shift in what developers should expect from coding agents. They write code, and they also observe the environment that code runs in. Sometimes that environment is compromised.
The Double-Edged Sword
The same access that let Claude Code find the miner could, in the wrong setup, let a malicious instruction do harm. An agent that can stop launch items can also create them. That tension explains why investors keep backing AI agent security startups as agents move deeper into developer machines.
So the takeaway isn’t “let agents run your security.” It’s narrower:
- Agents with system visibility can surface anomalies humans tune out.
- Permission gates turn that visibility into a safe asset rather than a liability.
- Dedicated security tools still close the loop. UntilHEX ran Malwarebytes for a reason.
XMRig on Macs Isn’t New
XMRig is legitimate software that miners install on purpose. Attackers like it for the same reason: it’s free, efficient, and easy to repackage. Mac cryptojackers built on XMRig date back to at least 2018, when Malwarebytes traced one to a renamed process that spread through fake installers and pirated downloads.
How UntilHEX’s Mac got infected remains unknown. The pattern, though, is familiar. Cracked apps, sketchy downloads, and fake updaters remain the usual entry points.
Quick Check: Is Your Mac Mining for Someone Else?
- Open Activity Monitor and sort by % CPU. Unknown processes near the top deserve a search.
- Review Login Items in System Settings → General → Login Items.
- Inspect launch folders:
~/Library/LaunchAgents,/Library/LaunchAgentsand/Library/LaunchDaemons. - Watch for symptoms: constant fan noise, battery drain, and heat at idle.
- Run a reputable scanner after any manual or agent-led cleanup.
The Bottom Line
Claude Code wasn’t built as an antivirus, and it shouldn’t replace one. This incident still shows what well-designed agents look like on a real machine. They notice what’s off, say so plainly, and ask before touching anything that matters. The temperature monitor app still got built. It just shipped with a much cooler Mac.
Related: Windows Search AI Agent: Is Microsoft Replacing Traditional Search?

Maliha
AI is moving steadily from experimental technology into the products and workflows people rely on every day. Maliha Irfan is a technology writer covering artificial intelligence, automation, and emerging software. Her work focuses on the practical side of AI agents, exploring how these systems are being used, what they can realistically accomplish, and the limitations that matter when businesses and individuals adopt them.
More from Maliha →